Kodem AI
Use Kodem AI as the anchor for a real shortlist.
Instead of returning to a broad directory, jump straight into the strongest adjacent matchups for pricing, workflow fit, and differentiation.
Overview
Overview
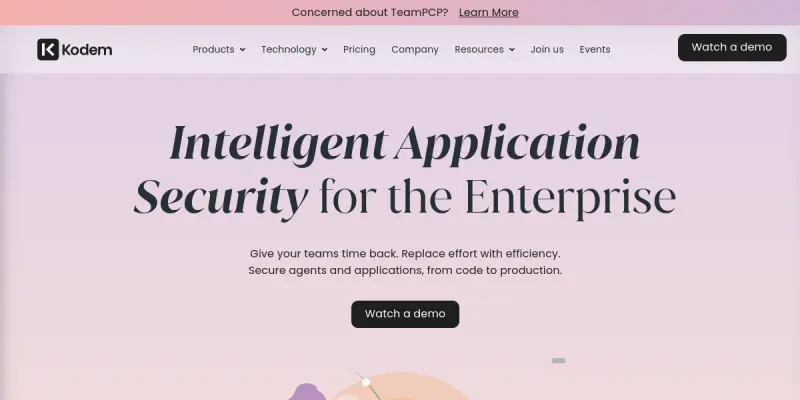
Kodem AI is an application security platform that introduces runtime-powered intelligence to traditional static and container security analysis. Instead of relying solely on static scanning, Kodem observes how applications actually behave during execution, which helps developers and security teams surface real, exploitable vulnerabilities while drastically reducing false positives. It integrates seamlessly into CI/CD pipelines and developer workflows, making it suitable for agile teams looking for accuracy without slowing down development.
Key Features
- Runtime-powered Scanning: Combines real-time application behavior with static code analysis to identify genuine vulnerabilities.
- Comprehensive Coverage: Supports SCA (Software Composition Analysis), SAST (Static Application Security Testing), Container scanning, and Infrastructure as Code (IaC) scanning.
- Low False Positive Rate: By verifying vulnerabilities against runtime context, Kodem filters out noise that typical static tools produce.
- CI/CD Integration: Plugs into common build and deployment pipelines to continuously monitor and secure code.
- Developer-first Workflow: Provides actionable, prioritized findings directly in the developer’s IDE or pull request comments.
- Correlation Engine: Maps runtime behaviors to code paths, enabling precise root-cause analysis.
Use Cases
Continuous Integration Security
Kodem can be added to any CI/CD pipeline (e.g., GitHub Actions, Jenkins, GitLab) to automatically scan every code commit and container image. Developers receive immediate feedback about security issues, preventing vulnerable code from reaching production.
Legacy Application Auditing
For existing applications with large codebases, Kodem’s runtime context helps differentiate between exploitable vulnerabilities and theoretical issues, allowing teams to prioritize remediation effectively.
Compliance and Policy Enforcement
Security teams can define custom policies based on runtime behavior and enforce them across multiple repositories, ensuring compliance with standards like OWASP Top 10, PCI-DSS, or SOC 2.
Container and Infrastructure Security
Kodem scans Docker containers and Kubernetes configurations for misconfigurations and known vulnerabilities, correlating them with runtime signals to reduce alert fatigue.
Pricing & Plans
Kodem AI is currently available as a free tier for small teams and individual developers. A paid enterprise plan with advanced features, dedicated support, and custom integrations is also offered. For specific pricing details, users should contact Kodem’s sales team directly.
Integrations & Compatibility
- CI/CD: GitHub Actions, GitLab CI, Jenkins, CircleCI
- IDEs: VS Code extension, JetBrains plugin (IntelliJ, PyCharm)
- Container Registries: Docker Hub, Amazon ECR, Google Container Registry
- IaC Tools: Terraform, CloudFormation
- Issue Trackers: Jira, GitHub Issues, GitLab Issues
Who Is It For?
Kodem is designed for software developers, DevSecOps engineers, and security analysts who need accurate, actionable vulnerability detection without slowing down development velocity. It is especially valuable for organizations with complex microservice architectures or regulatory compliance requirements.
Limitations
- Requires Runtime Access: To enable runtime analysis, the application must be running in a test or staging environment, which may not always be possible during early development.
- Learning Curve for Custom Policies: Creating custom security policies may require familiarity with Kodem’s policy language, which could be a barrier for non-security experts.
- Limited Public Documentation: As a relatively new platform, comprehensive public documentation and community resources are still growing.
Final Verdict
Kodem AI is a promising tool that redefines application security by bringing runtime context to static and container scanning. Its focus on reducing false positives and developer-friendly integration make it a strong addition to any security toolchain. While it is still maturing and has some limitations around documentation and runtime requirements, its free tier allows teams to evaluate its value with minimal risk.
Tool Facts
Screenshots & Interface
Pros
- ✓ Runtime intelligence reduces false positives by verifying vulnerabilities against actual application behavior.
- ✓ Integrates directly into CI/CD pipelines and developer IDEs for seamless workflow integration.
- ✓ Covers multiple security domains (SAST, SCA, container, IaC) in a single platform.
- ✓ Free tier available for small teams or individual evaluation.
Cons
- × Requires runtime access to the application, which may not be feasible in early development or offline environments.
- × Custom policy creation has a learning curve that may deter non-security-focused users.
- × Public documentation and community resources are still limited compared to more established tools.
How to Use Kodem AI in Your Workflow
Integrating Kodem AI into your professional toolkit enhances efficiency by automating manual steps. By configuring it to suit your specific project requirements, you can optimize output quality and reduce project cycle times. Standard workflows involve testing the tool on simple tasks before scaling its use to complex operations.
Frequently Asked Questions
What is Kodem AI used for?
Kodem AI is a runtime-powered application security platform that merges dynamic runtime intelligence with static analysis (SAST, SCA, container and IaC scanning). It helps developers and security teams identify and fix vulnerabilities with high accuracy and low false positives.
What is the pricing model for Kodem AI?
Kodem AI uses a Free pricing model.
What are the main advantages of Kodem AI?
The key benefits of Kodem AI include: Runtime intelligence reduces false positives by verifying vulnerabilities against actual application behavior., Integrates directly into CI/CD pipelines and developer IDEs for seamless workflow integration., Covers multiple security domains (SAST, SCA, container, IaC) in a single platform., Free tier available for small teams or individual evaluation..
What are the main limitations of Kodem AI?
Some limitations or cons of Kodem AI are: Requires runtime access to the application, which may not be feasible in early development or offline environments., Custom policy creation has a learning curve that may deter non-security-focused users., Public documentation and community resources are still limited compared to more established tools..
Alternative AI Tools
Cursor
Cursor Software AG provides a comprehensive CRM and BPM suite for customer relationship and business process management.
AskCodi
AskCodi is an AI-powered code assistant that helps developers generate code snippets and debug issues across multiple programming languages.
VictorOps AI
Splunk On-Call (formerly VictorOps) automates on-call operations and incident management for DevOps teams using AI-driven insights.
Rating Details
Based on 0 ratings
Quick Comparisons
Related Tools
More AI tools from the same workflow, industry, or category.
AICode
AICode is a spec-driven AI coding copilot for developers using Visual Studio Code. It enforces a disciplined workflow to prevent AI-generated technical debt and ensures maintainable code. Its key differentiator is forcing line-by-line human review before changes are applied.
Opik
Opik is an open-source platform for LLM observability and evaluation. It helps developers trace, test, and monitor AI applications and autonomous agents throughout development and production.
PlanetScale AI
PlanetScale provides serverless cloud hosting for Vitess and PostgreSQL databases. It targets developers and engineering teams requiring high-performance, scalable database infrastructure. The platform enables instant scaling and branching workflows.
CodeReview AI
CodeReview AI is a tool that uses artificial intelligence to analyze code and suggest improvements. It helps developers identify bugs, security issues, and style inconsistencies automatically. The tool integrates with popular version control systems to fit into existing workflows.
Reviews
No reviews submitted yet. Be the first to share your experience.
Write a Review
Share Your Experience
Join the community to write reviews, submit ratings, and bookmark your favorite AI tools.